651
raw candidates surfaced per pass on a mid-size monorepo
3
reach your team — each with evidence and a proof of concept
100%
of git history and every branch searched for secrets
24/7
continuous re-scan as advisories and code change
IaC scanning
Three “medium” misconfigs. One critical breach.
Terraform, Kubernetes, Docker and CloudFormation. Resource-graph reasoning chains multi-hop paths from a public endpoint to your data — and ranks them by what they actually reach.
◇Graph reasoning across resources, not per-file rules
◇Multi-hop paths from internet to data store
◇Severity by blast radius, not by rule class
The problem
Four tools, four queues, and nobody reading any of them.
How it works
From repository to proof, in five passes.
01
Comprehend
Reads the repository and builds a model of the application and its infrastructure.
02
Map the surface
Finds every route, entry point, credential and trust boundary.
03
Trace
Follows untrusted input across files, and resources across the infra graph.
04
Chain
Connects findings across domains into multi-step attack paths.
05
Verify
Tries to kill every candidate. Only survivors ship, each with a PoC.
Capabilities
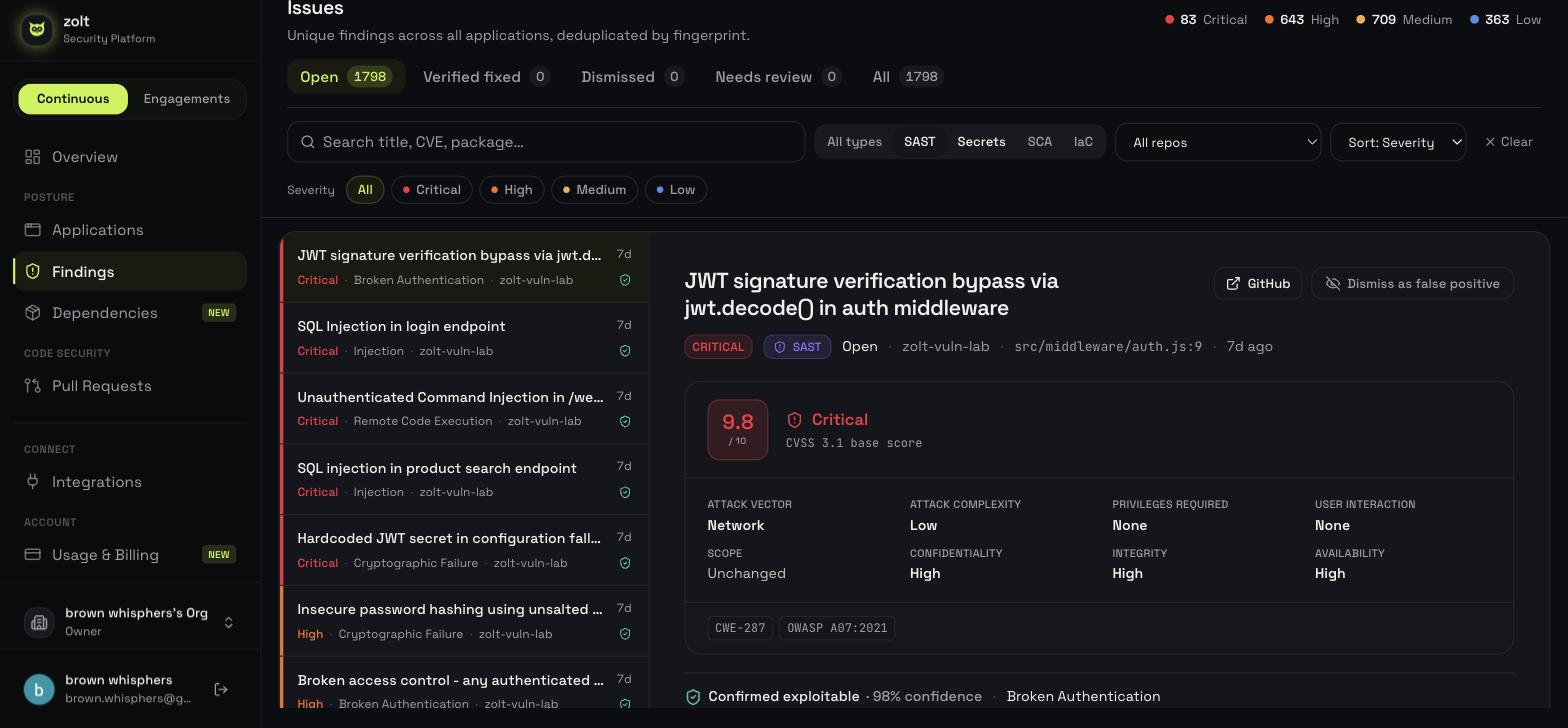
In the product
One queue, ranked by what is actually exploitable.
Findings from all four domains land in a single view with evidence, trace, and proof of concept attached.
FAQ
Code security, in detail.
How is this different from running four separate scanners?
The engines are only the recall layer. One agent reads all four streams against a single model of your application, which is what makes cross-domain chaining and reachability possible — and what lets it delete the 648 candidates that are not real.
What languages and frameworks are supported?
Go, TypeScript and JavaScript, Python, Java, Ruby, PHP, C# and Rust for code analysis; npm, PyPI, Go modules, Cargo and Maven for dependencies; Terraform, Kubernetes, Docker and CloudFormation for infrastructure.
Does it need production access?
No. Read-only repository access through a GitHub App you control, scoped to the repositories you choose, revocable at any time.
How noisy is the first scan?
The first pass surfaces the most because it covers your full history. After the adversarial pass, a mid-size monorepo typically produces a handful of verified findings, not hundreds.